About Enable Security
Enable Security is a security consultancy that tests and secures VoIP, SIP and WebRTC systems for cloud communications companies, including CPaaS, UCaaS and contact centre platforms, carriers and VoIP providers. We believe communication is a fundamental human need, and securing it lets people communicate freely.

Who are we?
We are a team of security researchers who strive to provide valuable results through quality work. We are curious, keep learning, and share what we find with the security community. We value honesty and say things as we see them. And naturally, we do love a tough challenge.
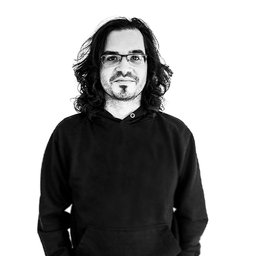
Sandro Gauci
Sandro Gauci founded Enable Security back in 2008 and nowadays leads its operations and research. To the real-time communications community he is known as the original developer of SIPVicious OSS. His role is to focus on the vision of the company, design offensive security tools and engage in security research and testing. Therefore, he is the proud owner of the title of Chief Mischief Officer at Enable Security.
Sandro started his career in information security back in 2000 and has been hacking software and phone systems since his teens.
He offers public office hours and is reachable here.
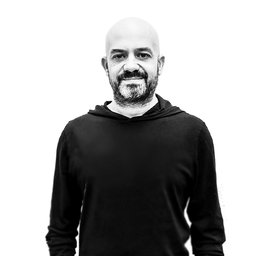
Alfred Farrugia
Alfred Farrugia leads development of our in-house security testing tools, does reverse engineering, fuzzing, DoS simulation and security research. He is an amazing pentester and often finds denial-of-service vulnerabilities where least expected. Hence he is the proud owner of the title of Chief Demolition Officer at Enable Security.
After working in highly regulated environments in finance, Alfred turned his passion to understanding and breaking applications through fuzzing techniques and manual code analysis.
What makes Enable Security different
RTC focus since 2007
Sandro Gauci published SIPVicious in 2007, a year before founding Enable Security. VoIP and WebRTC security has been our focus ever since, backed by tools we build ourselves.
Original research
Over 35 security advisories in RTC software such as Asterisk, FreeSWITCH, OpenSIPS, Kamailio, rtpengine and coturn. That research feeds into every test.
Production or staging
Our DDoS tests can run against live production systems, coordinated with your team, or against staging and other non-production environments.
Our own name
Every engagement is run by our own researchers and delivered under the Enable Security name, never white labelled. Trusted subcontractors join only when needed.
Who we work with
Our clients, mainly in the US and Europe, range from venture-backed scale-ups to publicly listed companies.
CPaaS and UCaaS
Communications API platforms and cloud PBX vendors, hosted or on-premises.
Contact centres
CCaaS and customer engagement platforms.
Carriers
Carriers, VoIP providers, SIP trunking and DID providers.
Regulated sectors
Emergency and public safety communications providers, banks and fintech companies.
How Enable Security works
Scoping and proposal
A call to understand your platform and goals, followed by a proposal covering scope, timeline and cost.
Kickoff
We agree on access, contacts and test windows, especially for testing on production systems.
Testing
We work directly with your engineers by email, Slack or your own tools, plus scheduled calls. We typically respond within one working day.
Report and retest
Every finding comes with a reproducible proof of concept, and we retest your fixes.
Key facts about Enable Security
- Company
- Enable Security GmbH, registered at Amtsgericht Berlin-Charlottenburg, HRB 173016 B (Impressum)
- Type
- Security consultancy focused on real-time communications: VoIP, SIP, WebRTC and related protocols such as RTP, SRTP, DTLS and TURN
- Founded
- 2008 in Malta, trading as Enable Security ever since. Incorporated in Germany as Enable Security GmbH in December 2015.
- Founder
- Sandro Gauci, original developer of SIPVicious OSS
- Headquarters
- Passau, Germany
- Services
- VoIP penetration testing, WebRTC penetration testing, VoIP security assessment, DDoS testing, fuzz testing, code and configuration review, consultancy
- Communication
- Email, Slack or the client’s own tools, plus scheduled calls. Typical response time is one working day.
- Clients
- CPaaS, UCaaS and contact centre platforms, carriers and VoIP providers, emergency communications providers, and fintech. From venture-backed scale-ups to publicly listed companies. Work is delivered under our own name, never white labelled.

Blog


Research and publications

RTCSec Newsletter